Greinfort / Active Incident Response
When detection isn't enough, take action.
From alert to containment: traffic blocking, firewall integration and configurable automation to respond before an incident escalates.
Firewall integration • Malicious traffic blocking • Informational, supervised and automatic modes • Action traceability • Full operational control
What happens between the alert and the decision?
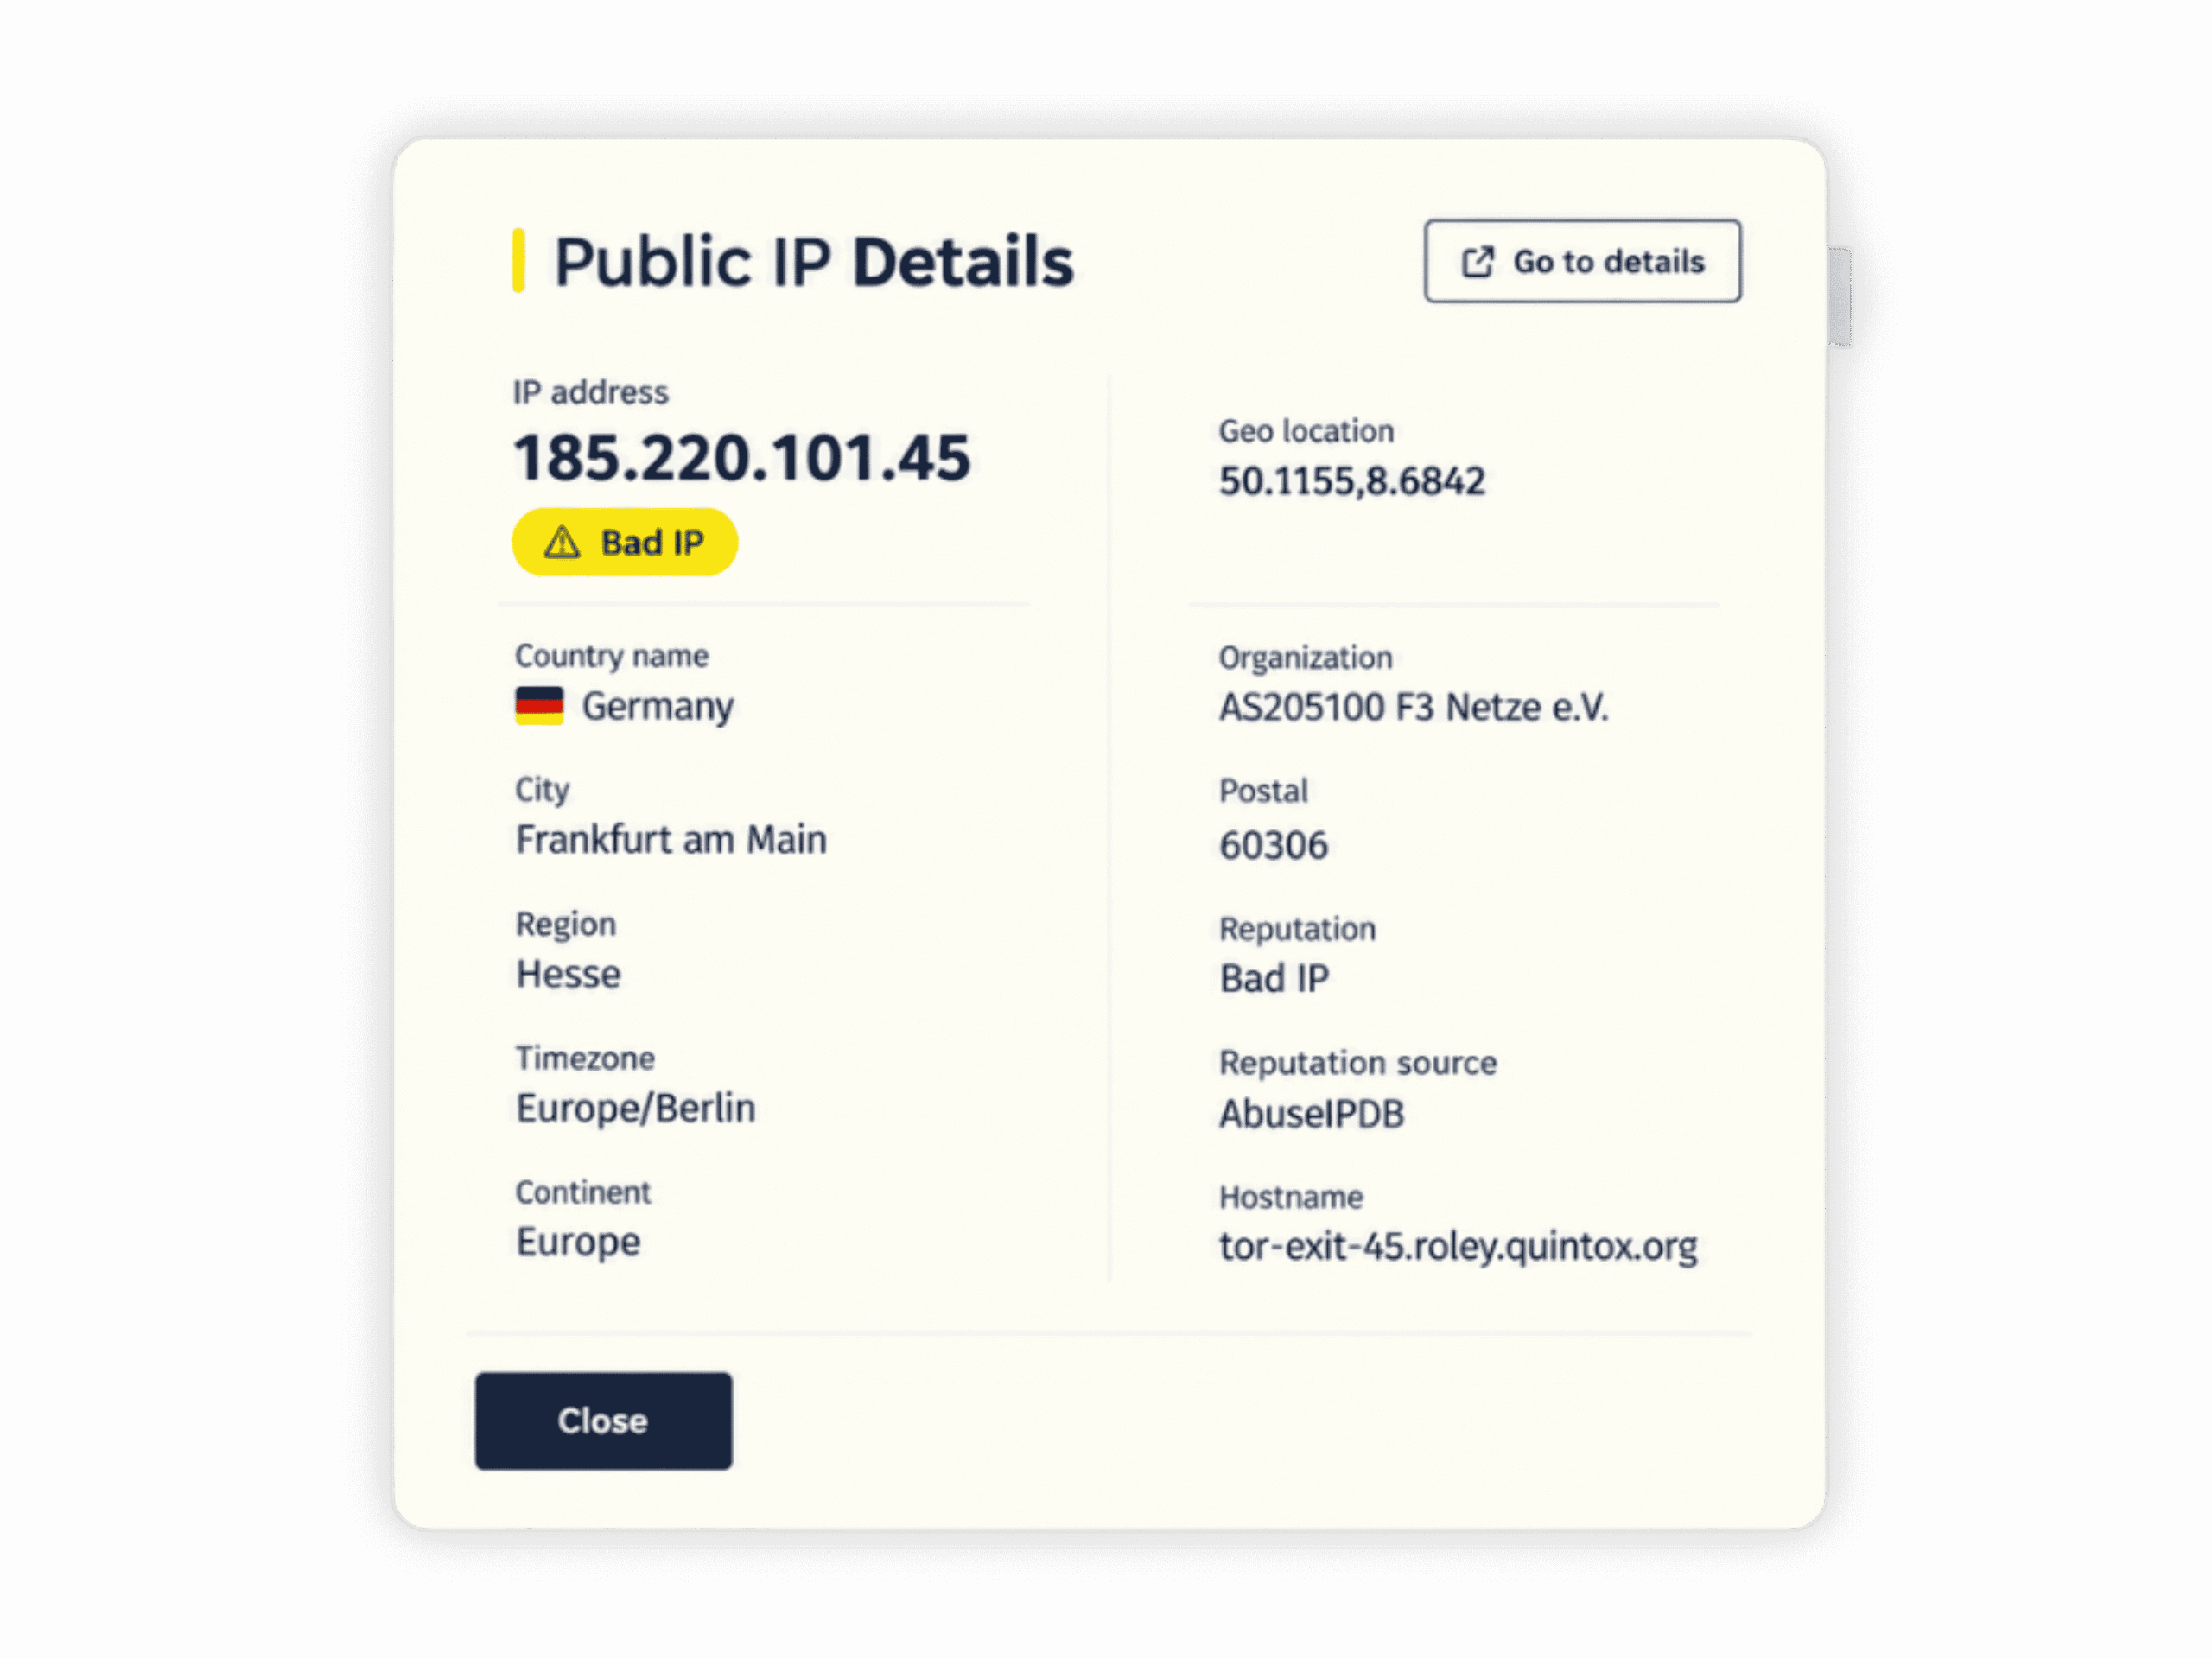
In many incidents, the critical time is not detection but response. A malicious outbound connection may be routine scheduled work from a supplier — or an unauthorised communication belonging to an active threat that can continue to progress while teams review evidence, validate impact and coordinate action.
The capability
Full control over every response action.
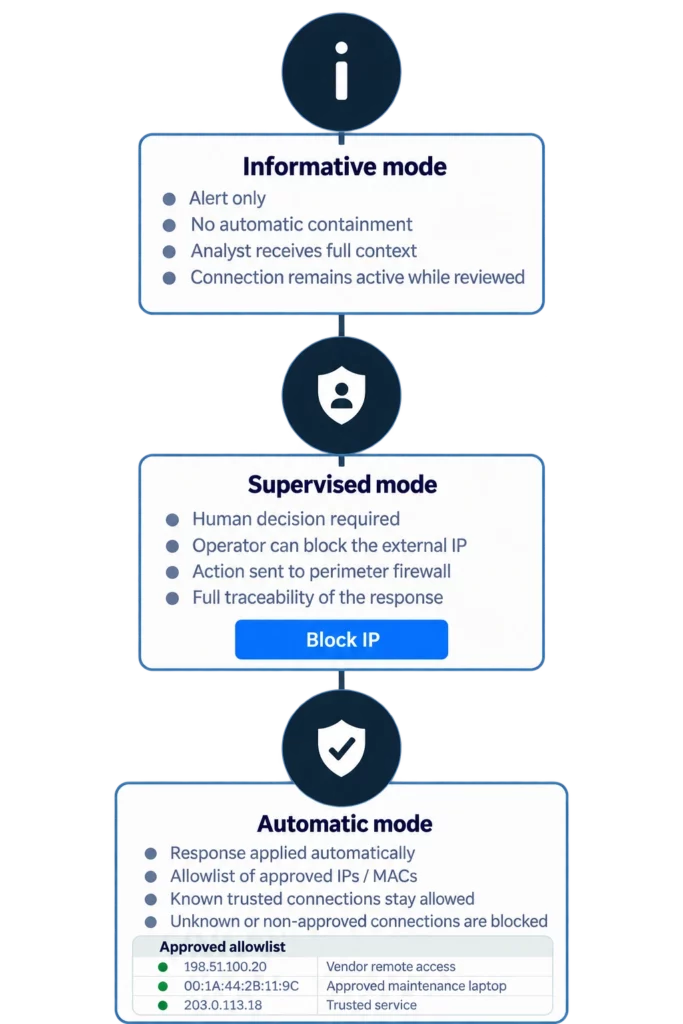
Greinfort can integrate with firewalls (Fortinet, Palo Alto, Check Point, Stormshield and OPNsense) to block malicious external connections to or from the industrial network.
Response policy can be adapted to each organisation’s maturity and confidence level: informational, supervised or automatic.
Less exposure time
Greinfort helps move from detection to response while maintaining operational control and reducing the time required to contain active threats.
Less exposure time
Controlled response
Operational protection
OT response must be controlled, traceable and proportionate.
The goal is not reckless automation. It is to reduce exposure time while maintaining operational control. Greinfort enables faster response without losing the caution required in an industrial environment.