GREINFORT – OT CYBERSECURITY PLATFORM
Visibility and control across your industrial OT network
OT visibility. Monitoring. Security alert and vulnerability detection. Active response. Non-disruptive. Automated. Up and running in less than a day.
How we protect your operations
Every module solves a real-world problem.
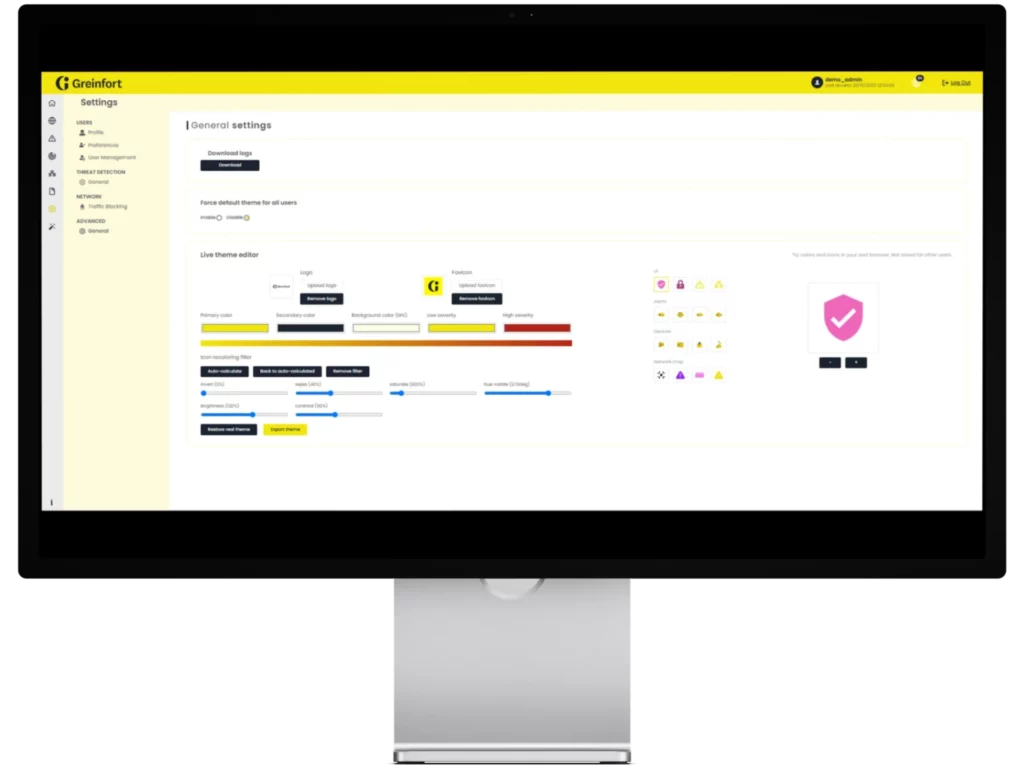
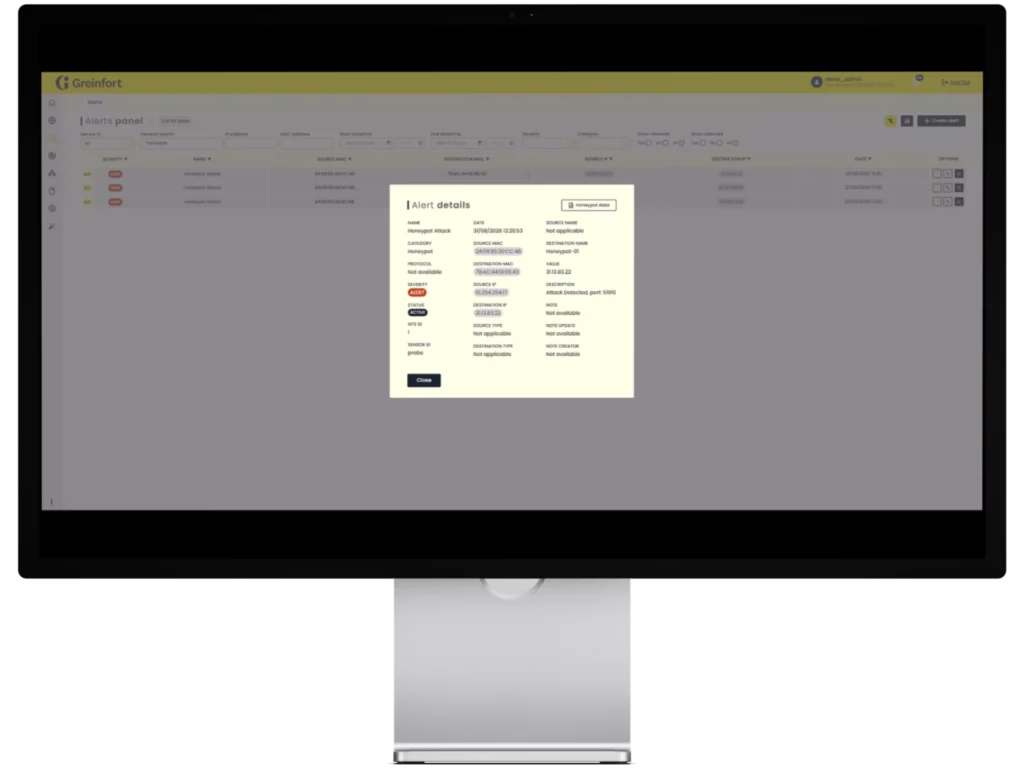
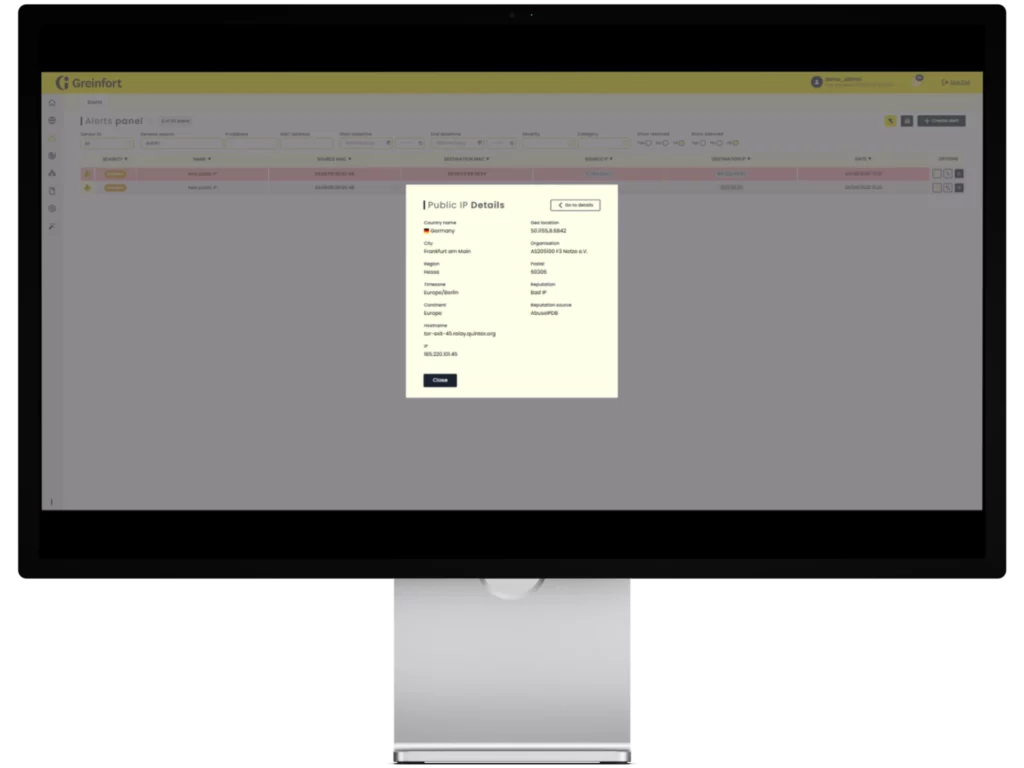
Dashboard
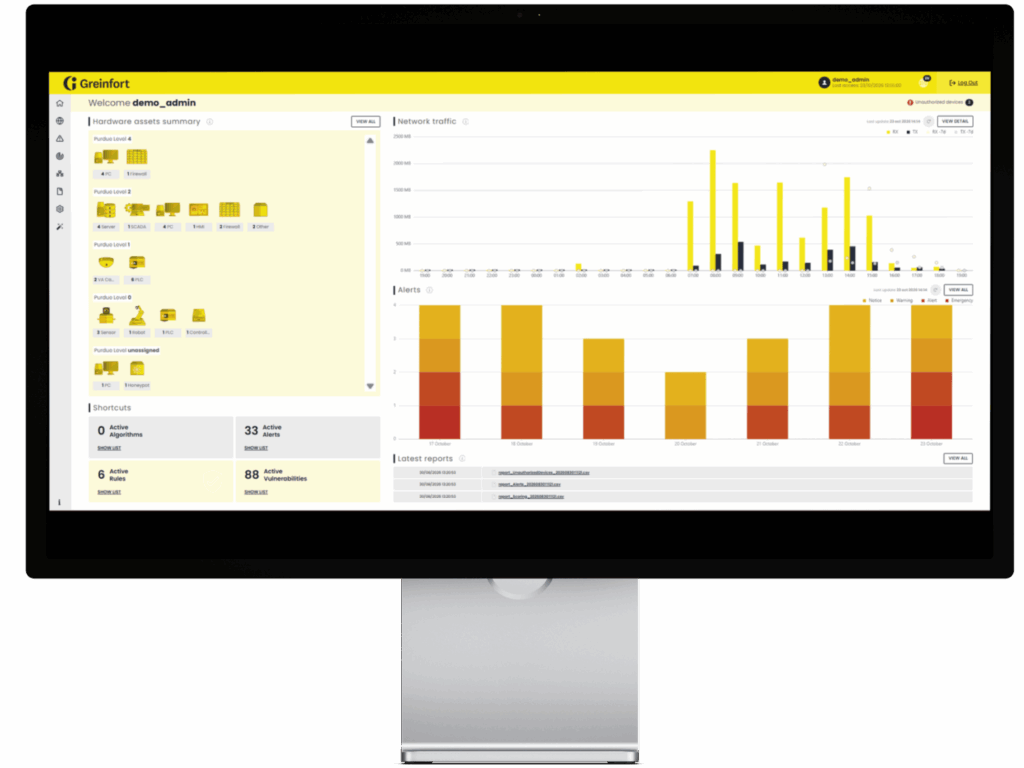
A dynamic dashboard bringing together the key information needed for a global view and continuous monitoring of the security posture across the entire industrial plant.
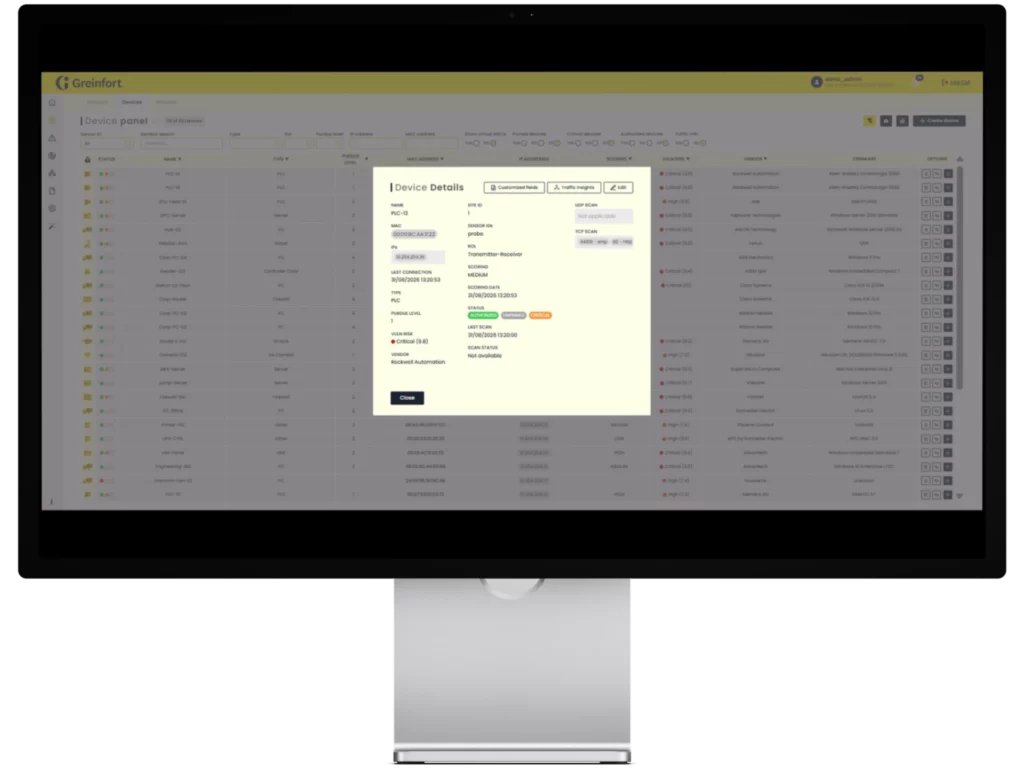
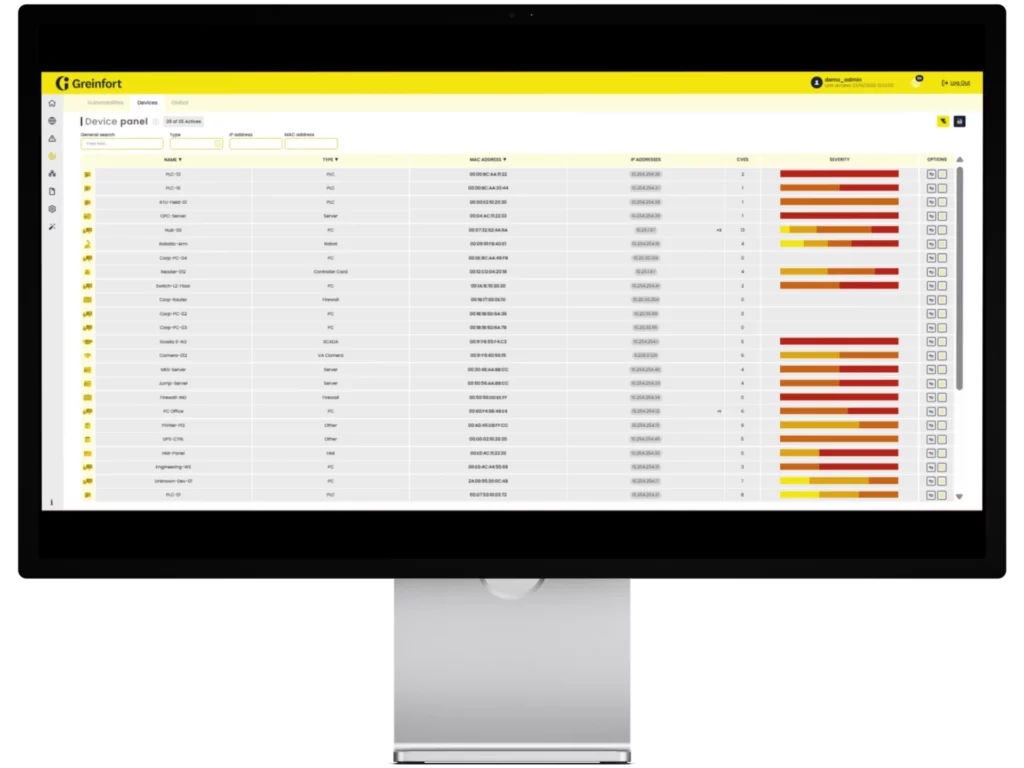
Network Asset Inventory
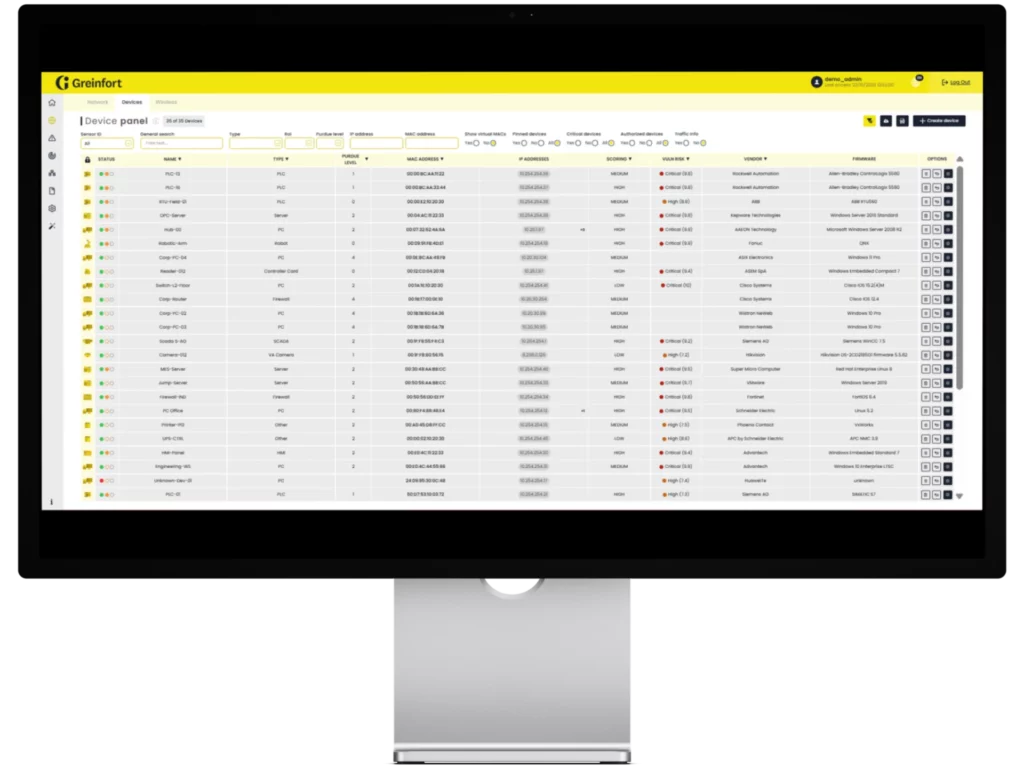
Automatic discovery of all connected assets: IP, MAC, manufacturer, device type, firmware, operating system, open ports, services and more. Non-disruptive.
- Automatic discovery and tagging.
- Editable properties and custom fields
- Filterable and exportable – audit-ready.
- Linked to the network map, alert manager and vulnerability management.
Real-Time Network Map
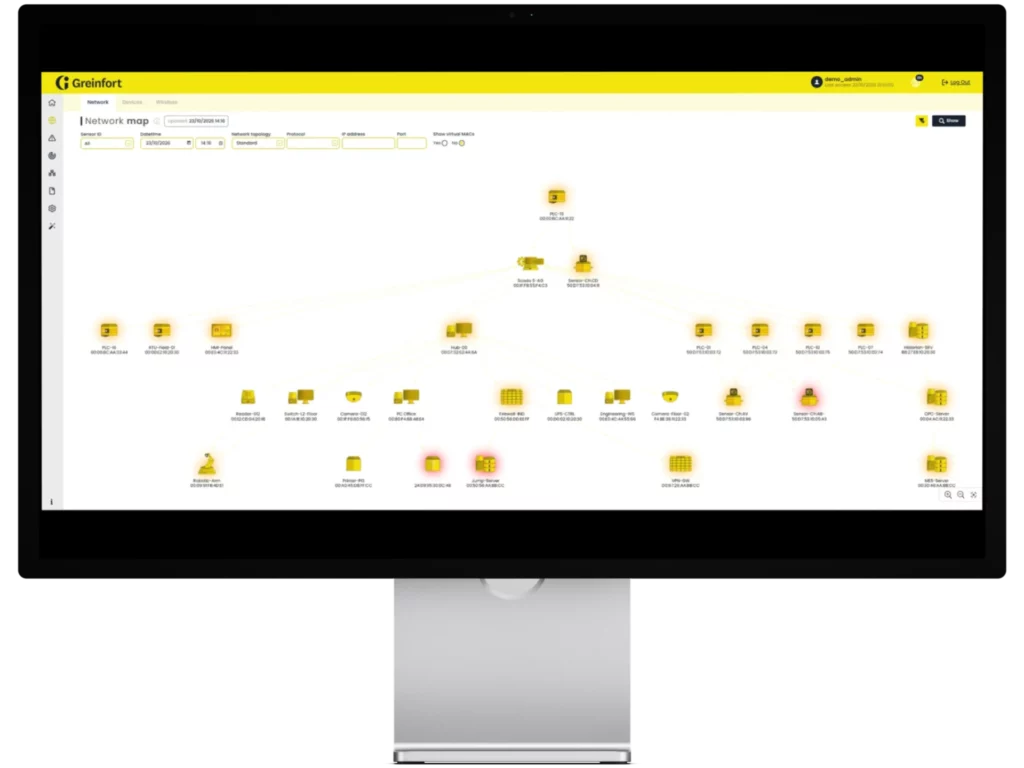
Automatic calculation of current or historical network topology. Visualises all devices, their active connections and communication flows. Newly connected devices are detected immediately.
- Visualise device-to-device connections.
- Drill down into asset information (click-through).
- Interactive topology with filters by protocol, asset type, subnet and more.
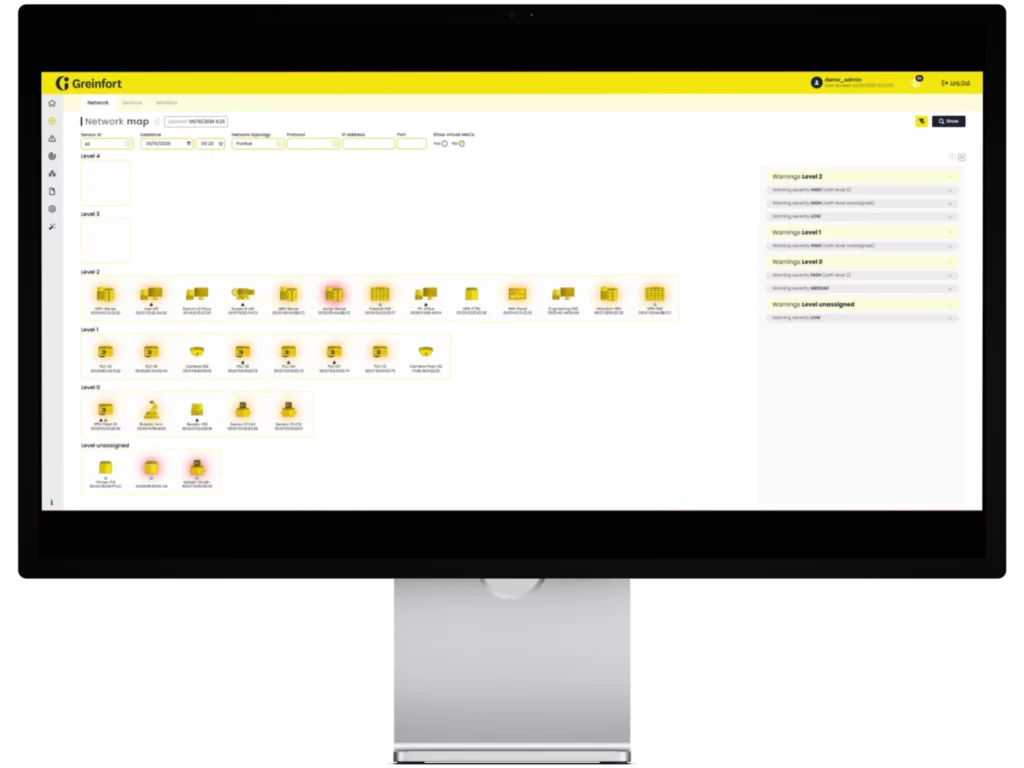
Purdue Map
A compliance-oriented view based on the ISA/IEC 62443 model. Devices are automatically classified by Purdue level, with severity-based alerts and detection of devices assigned to unexpected or incorrect levels.
- OT/ICS compliance perspective.
- Severity-based warnings and identification of deviations from good practice.
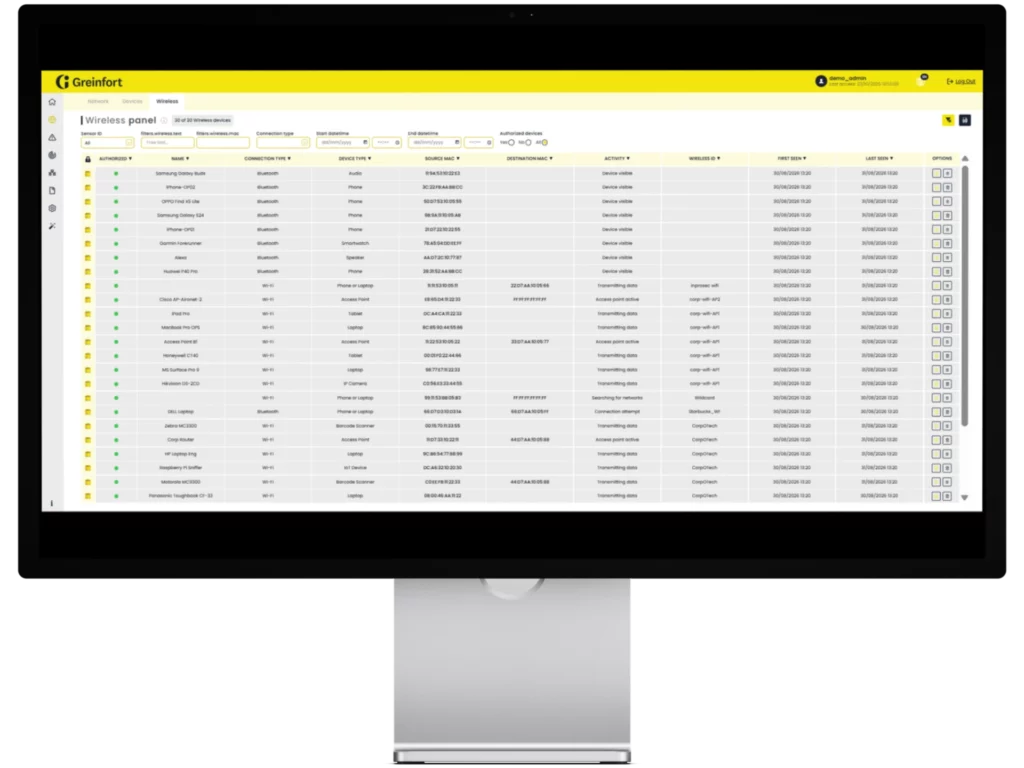
Air Watcher
Provides comprehensive visibility into wireless assets (Wi-Fi and Bluetooth) operating in the vicinity of traffic sensors, uncovering devices that remain invisible to traditional OT monitoring solutions. These unmanaged or unauthorized devices may introduce cybersecurity risks, violate security policies, or act as early indicators of potential operational safety incidents.
- Wireless devices detected in the vicinity of Greinfort probes.
- Connection Type.
- Device IDs, MAC addresses, device names, activity, and first/last seen timestamps.
- Visibility into newly detected wireless devices and anomalous behavior.
Smart View
Optional active scanner, which can be disabled at plant or device level, providing a more complete inventory.
- Detection of open ports and running services on OT assets.
Vulnerability Management
Identifies and prioritises vulnerabilities in OT assets using the NIST National Vulnerability Database (NVD). Includes CVE, CVSS, CWE and publication dates.
- Views by individual vulnerability, by plant node and global KPIs for tracking.
- Integration with commercial scanners to leverage existing subscriptions.
- Prioritisation based on CVE data and operational reality: which vulnerabilities are being actively exploited and which are associated with ransomware campaigns (CISA KEV).
Business Rules Engine
Allows the technical team to configure anomaly-detection strategies: detection thresholds, IDS tuning and machine-learning adaptation to the specifics of a network.
- Configuration and fine-tuning of individual detection techniques.
- Custom alert rule configuration.
- Machine learning model training tailored to each customer’s network environment.
Alert Manager
Security incident control centre. Alerts are generated through different strategies and presented with the information required for analysis and response.
- Active alerts categorized by severity level.
- Advanced search and filtering, alert muting and resolution, and note-taking capabilities.
- Complete alert history.
- Export-ready for SIEM integration and forensic analysis.
- Managed directly through the web interface or via API.
- Proactive email notifications with configurable alert severity and type-based criteria.
Industrial honeypot
A low-interaction decoy system placed artificially on the network. Like a canary in a coal mine, any interaction with it may indicate that an active attacker is probing the network.
- Low-interaction physical or virtualized honeypot appliance.
- Detects and logs adversary activity, including accessed URLs, executed commands, and variables read or modified.
Active Response
Blocks malicious external connections through direct integration with the customer’s perimeter firewall. Blocking policy is configurable: informational (notify only), manual (operator decides) or automatic (with safeguards).
- Automated threat intelligence and reputation assessment for external IP addresses.
- Three operating modes: Informational · Manual · Automatic.
- Supported integrations: Stormshield · Fortinet · Palo Alto Networks · Check Point · OPNsense.
- IP allowlist import and export.
Traffic Traceability
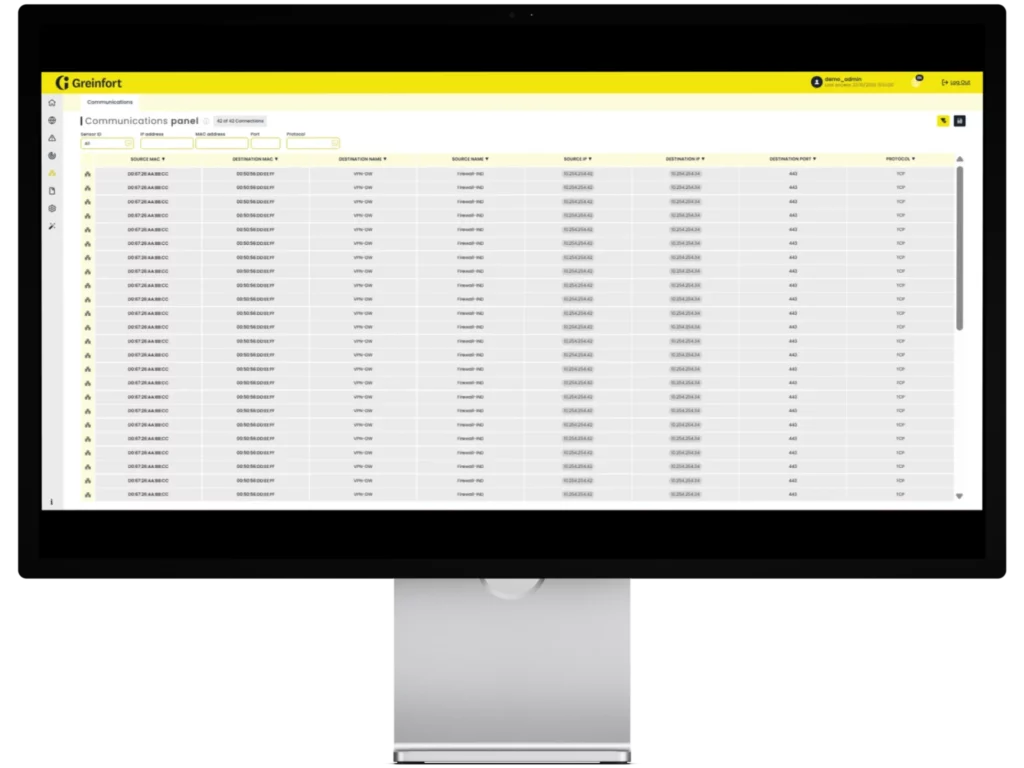
All network traffic is logged and grouped by source, destination, port and protocol, enabling detailed post-incident forensic analysis.
- Comprehensive network communication logs with identification of all devices involved.
- Filterable and exportable in CSV format.
- Supports incident response and digital forensic investigations.
Reports
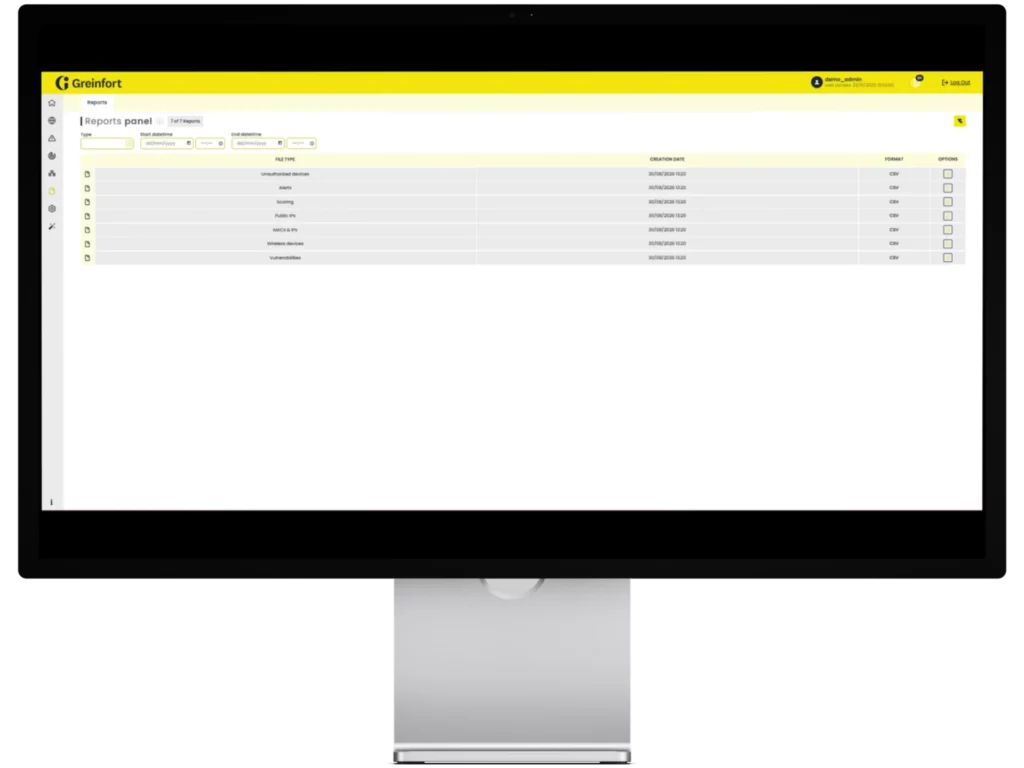
Automated, business-oriented reports with OT security KPIs. Designed to be understandable without specialist technical knowledge.
- Latest detected alerts.
- Unauthorized devices.
- Detected wireless assets.
- Contacted public IP addresses.
- MAC-to-IP address mappings.
- Device risk scoring.
- Vulnerabilities detected across the network.
Five Detection Engines
Five detection strategies. No single evasion path.
Static rules
Predefined suspicious activity detection rules covering new devices, new network connections, configuration changes, network scanning, and spoofing attempts (including Man-in-the-Middle attacks).
Premium signature-based IDS
Known attacks based on an automatically updated signature database powered by Cisco Talos threat intelligence.
Machine Learning
Learns normal behaviour patterns and detects previously unseen deviations in real time, including potential zero-day activity.
Process Mining + UEBA
Analyses industrial workflows and detects anomalies in production processes that may indicate manipulation or sabotage.
Industrial honeypot
Supported OT Protocols
Compatible with both established and modern industrial protocols:
EtherNet/IP
Modbus
BACnet
S7comm
PROFINET
IEC 60870-5-104
DNP3
GE SRTP
Emerson ROC+
Omron FINS
HART-IP
Mitsubishi CC-Link
IEC 61850 GOOSE
IEC 61850 SV
IEEE 37.118
ANSI C12.22
Niagara Fox
LLDP
EtherCAT
OPC UA
DHCP
and more…
Also supports common enterprise/network protocols:
DNS
mDNS
LLMNR
DHCP
SNMP
HTTP
HTTPS
SSH
FTP
TLS
NetBIOS
SMB
…
Three ways to deploy Greinfort. One for every environment.
Centralised on-premises
An OT subnet or a small enterprise where maximum privacy is required: traffic remains within the infrastructure.
Distributed on-premises
Multiple subnets or sites, with everything kept local and centrally managed from one interface.
Cloud
Lightweight sensors at the customer site, with application logic in Greinfort’s secure cloud. Best suited to scalability and multi-site management.
Simple, accessible and built for OT. No unnecessary complexity.
Greinfort was created with a clear vision: make OT protection accessible to industrial organisations of all sizes. It is designed to be efficient, easy to adopt and delivered through a network of specialised partners with close knowledge of industrial environments.
Designed to deliver value from day one, without unnecessary friction or complexity. An agile, intuitive solution that fits naturally into day-to-day operations and delivers practical results without requiring large teams or complex structures.
Enterprise alternatives
Deployment time
< 1 day
Weeks
Production impact
None
Potential impact
Required operator profile
OT operator
Security specialist
Pricing
Accessible for SMBs
Enterprise
Technology sovereignty (EU)
✓ 100% Galicia, Spain
✕ USA / ISR / RUS
Industrial honeypot
✓ Physical hardware / VM
Less common in the market
Air Watcher (Wi-Fi/BT)
✓ Wi-Fi + Bluetooth
OT network only
Contact Us
Complete the details and our team will tailor the demo to your industry, infrastructure and needs.